Security
Security settings
The Security section allows you to control access to your workspace and monitor the activity of all users. It includes three subsections: Access, Login History, and Audit Trail.
Controlling access
The Access subsection of the Security settings allows you to provide users with secure and convenient ways to access the workspace.
Access control
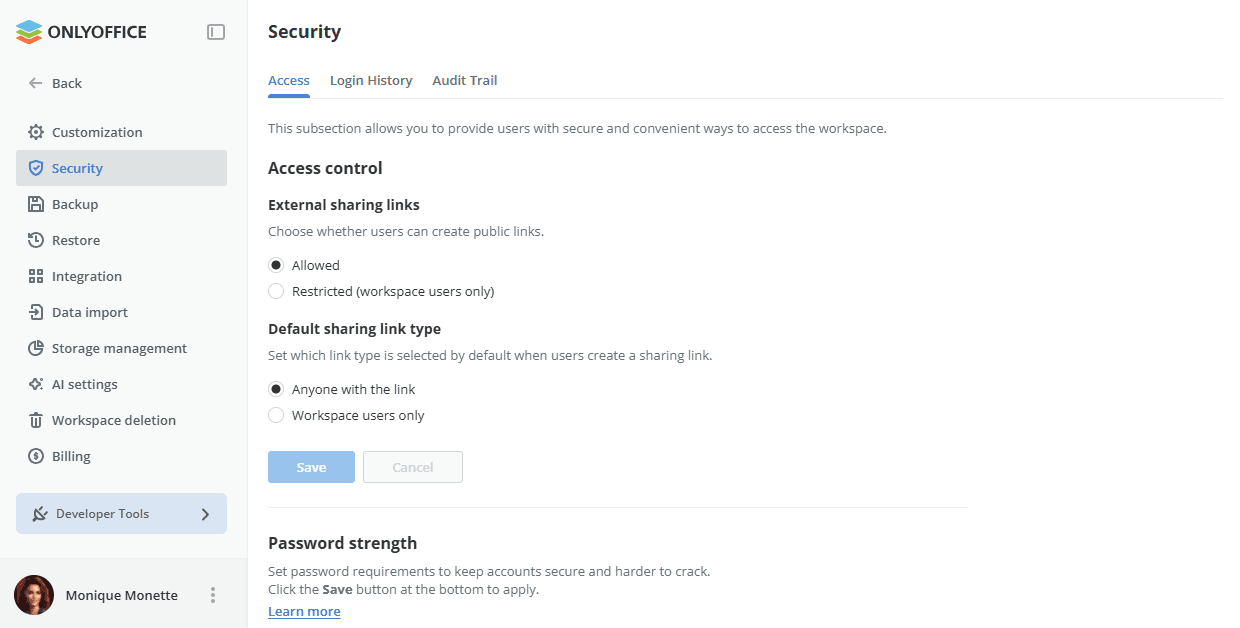
This section allows you to manage the sharing links that users can create:
- External sharing links - choose whether users can create public links: Allowed or Restricted (workspace users only).
- Default sharing link type - set which link type is selected by default when users create a sharing link: Anyone with the link or Workspace users only.
Click the Save button to apply the changes you made.
Password strength
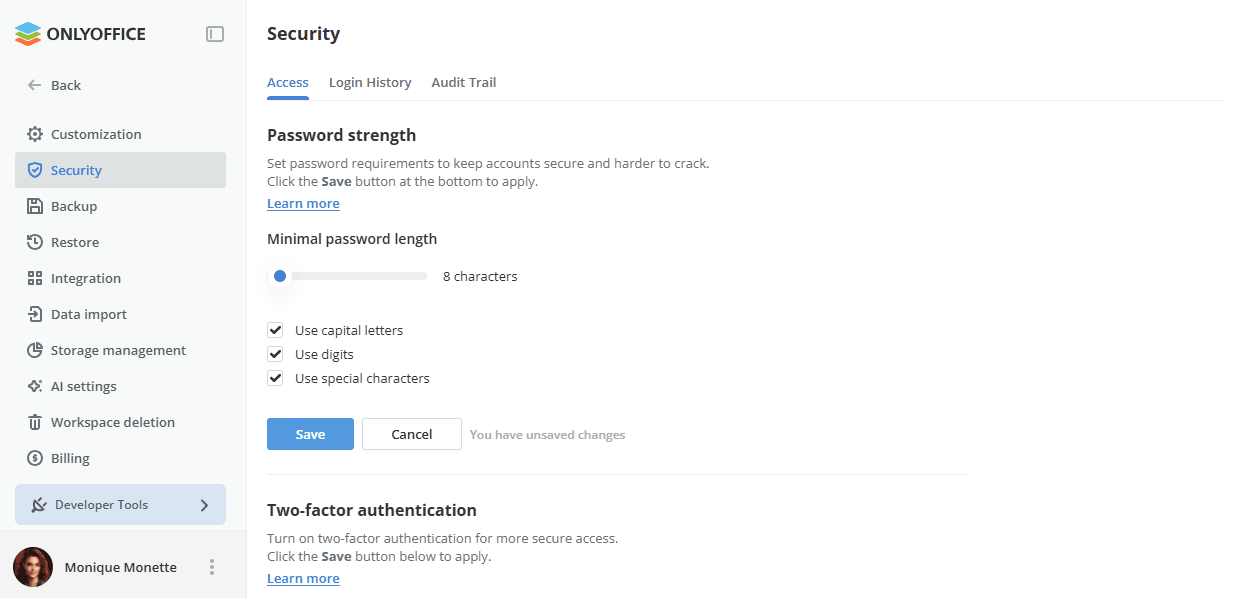
This section allows you to set password requirements to keep accounts secure and harder to crack. To do that,
-
use the Minimal password length bar to determine how long the password should be to be considered strong,
The password must be at least 8 but no more than 30 characters long.
-
check the appropriate boxes below the bar to determine the character set that must be used in the password: Use capital letters, Use digits, Use special characters,
-
click the Save button at the bottom of the section to apply the changes you made.
Two-factor authentication
This section allows you to turn on two-factor authentication with authenticator apps for more secure access.
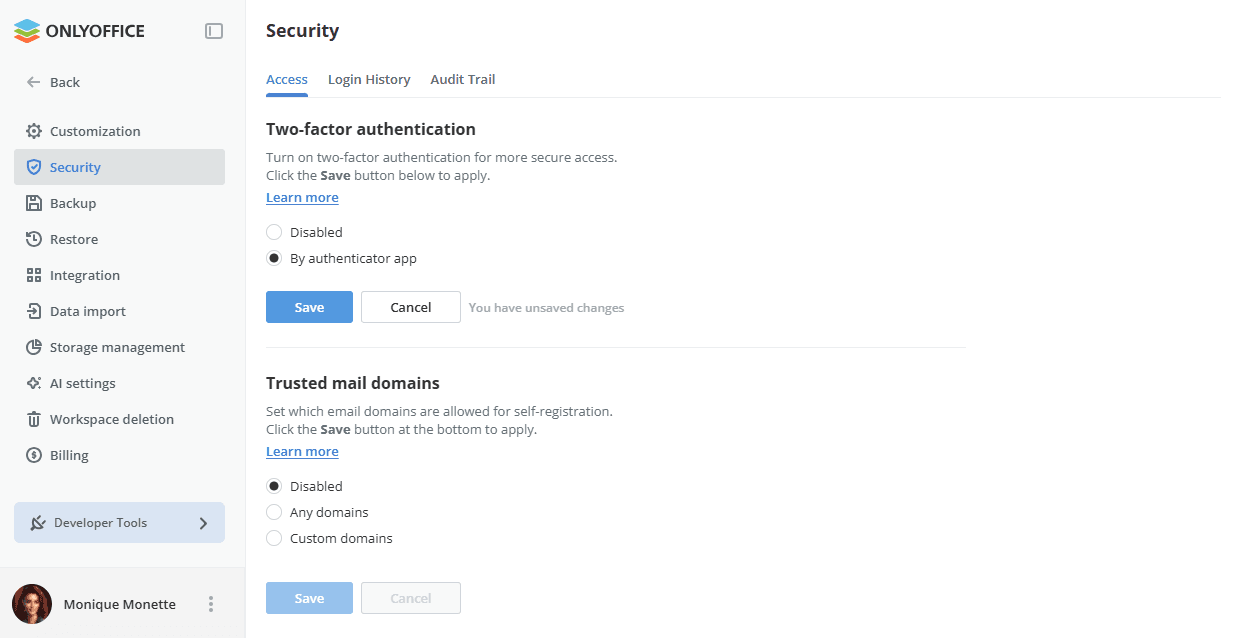
To enable two-factor authentication with an authenticator app,
- check the By authenticator app radio button under the Two-factor authentication section,
- click the Save button below to apply the changes you made.
When two-factor authentication with an authenticator app is enabled, a user can access the workspace data after entering their regular email and password or signing in via a social media account and typing in a six-digit verification code or a backup code generated by the authenticator app.
To access your workspace for the first time after enabling two-factor authentication:
- Enter your regular credentials to access your workspace. The QR code and your secret key are displayed on your login confirmation page.
- Install an authenticator app on your mobile device. You can use Google Authenticator for Android and iOS or Authenticator for Windows Phone.
- Open the authenticator app on your mobile device and configure it in one of the following ways:
- Scan the QR code displayed in the browser, or
- Manually enter your secret key displayed in the browser,
- On your login confirmation page, enter a 6-digit code generated by your application.
- Click the Connect app button.
To learn more on how to use two-factor authentication in your workspace, you can read the following article.
Trusted mail domains
This section allows you to set which email domains are allowed for self-registration in your workspace. By default, this option is disabled. To enable it,
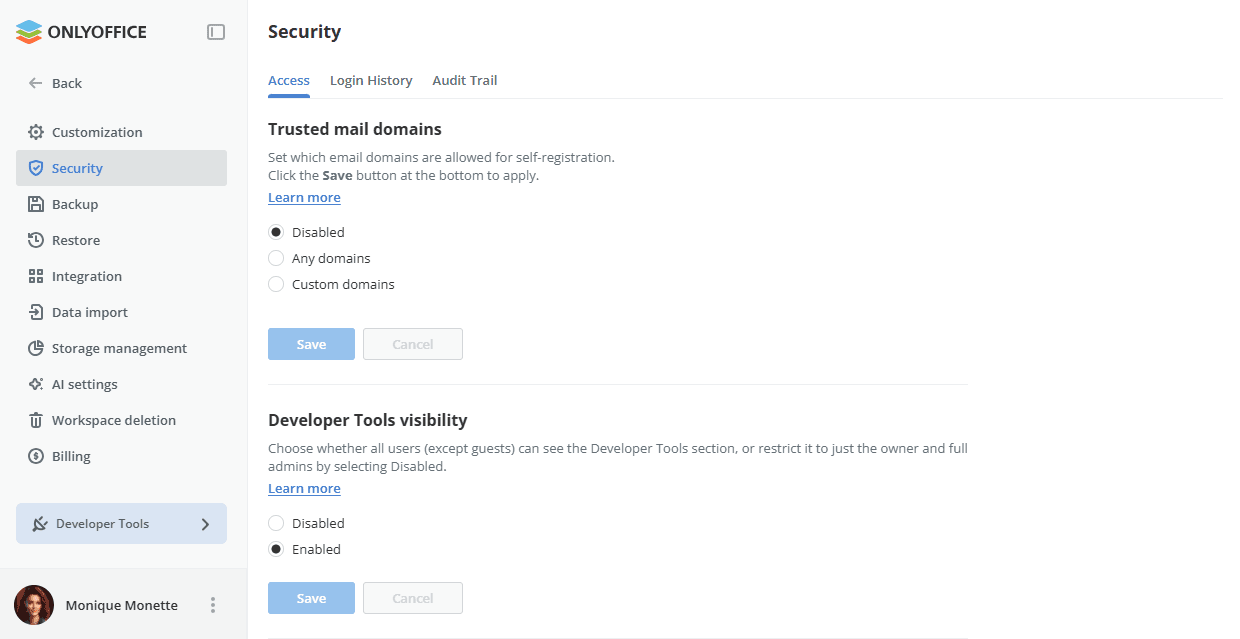
- check the Custom domains radio button,
- enter the trusted mail server in the field which appears below,
- click the Save button at the bottom of the section to apply the changes you made.
To allow self-registration from any email domain, check the Any domains radio button.
To add more mail servers, use the Add trusted domain link. To delete a server added by mistake, click the corresponding  icon to the right of the field.
After that, any user who has an account at a specified mail server will be able to register on their own by clicking the Click here to join link on the Sign In page and entering the email address. An invitation email with a link to the workspace will be sent to the specified email address. To sign in, the user will need to follow the link provided in the email, enter a password and confirm it.
To disable this option again, just check the Disabled radio button.
Developer Tools visibility
This section allows you to choose whether all users (except guests) can see the Developer Tools section, and accordingly create their own webhooks or OAuth 2.0 apps, etc. This setting is enabled by default.
Any user can access the Developer Tools section by clicking the corresponding link on the left panel.
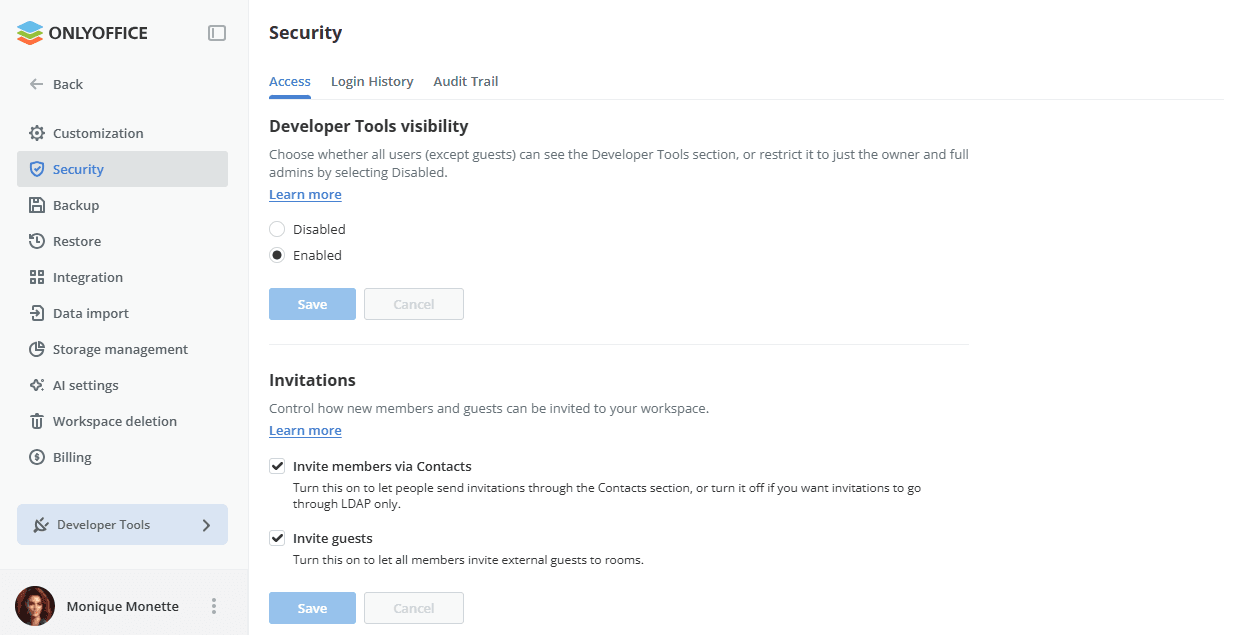
To restrict the Developer Tools section to the owner and full admins only,
- check the Disabled radio button,
- click the Save button at the bottom of the section to apply the changes you made.
Brute force protection
This section allows you to set a limit on failed login attempts to protect your workspace from brute-force attacks. Once the limit is reached, the associated IP address is temporarily banned or shown a CAPTCHA, if enabled.
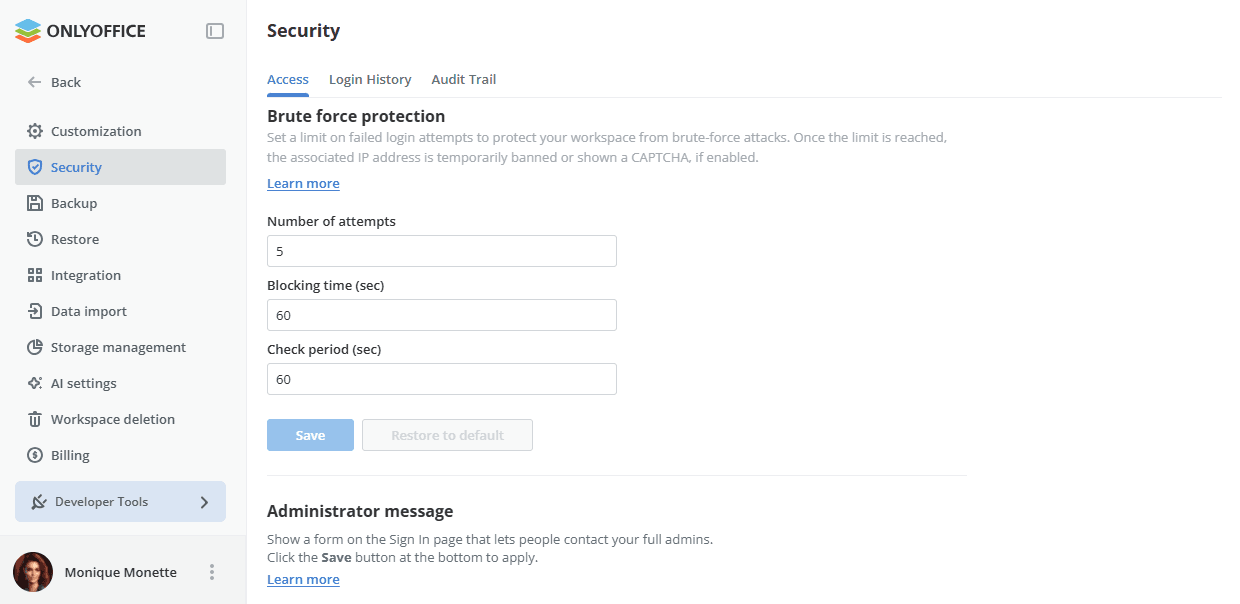
- in the Number of attempts field, set up the limit of unsuccessful login attempts by the user;
- in the Blocking time (sec) field, set up the time interval for blocking new login attempts;
- in the Check period (sec) field, set up the time interval for counting unsuccessful login attempts;
- click the Save button at the bottom of the section to apply the changes you made.
To return the fields to their initial values, use the Restore to default button.
By default, this feature is disabled in the server version. If you want to use it, it's necessary to enable the feature in the configuration file. To learn more, read the following article.
Administrator message
This section allows you to show a form on the Sign In page that lets people contact your full admins in case they have troubles while accessing the workspace.
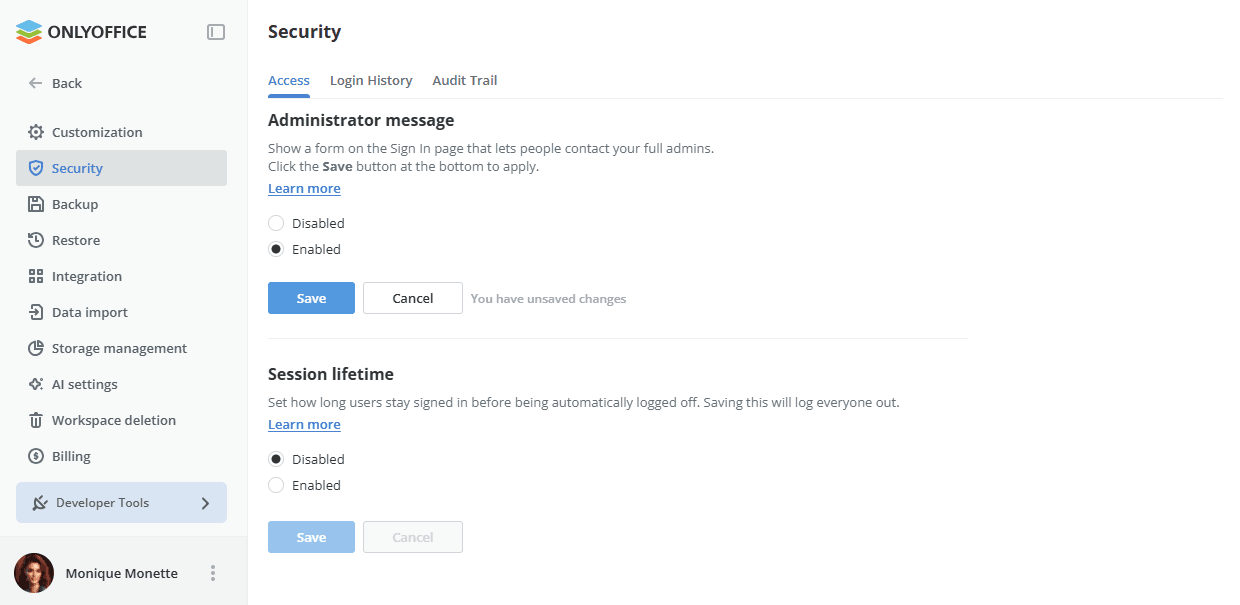
To enable it, just check the Enabled radio button and click the Save button at the bottom of the section to apply the changes you made.
Session lifetime
This section allows you to set how long users stay signed in before being automatically logged off.
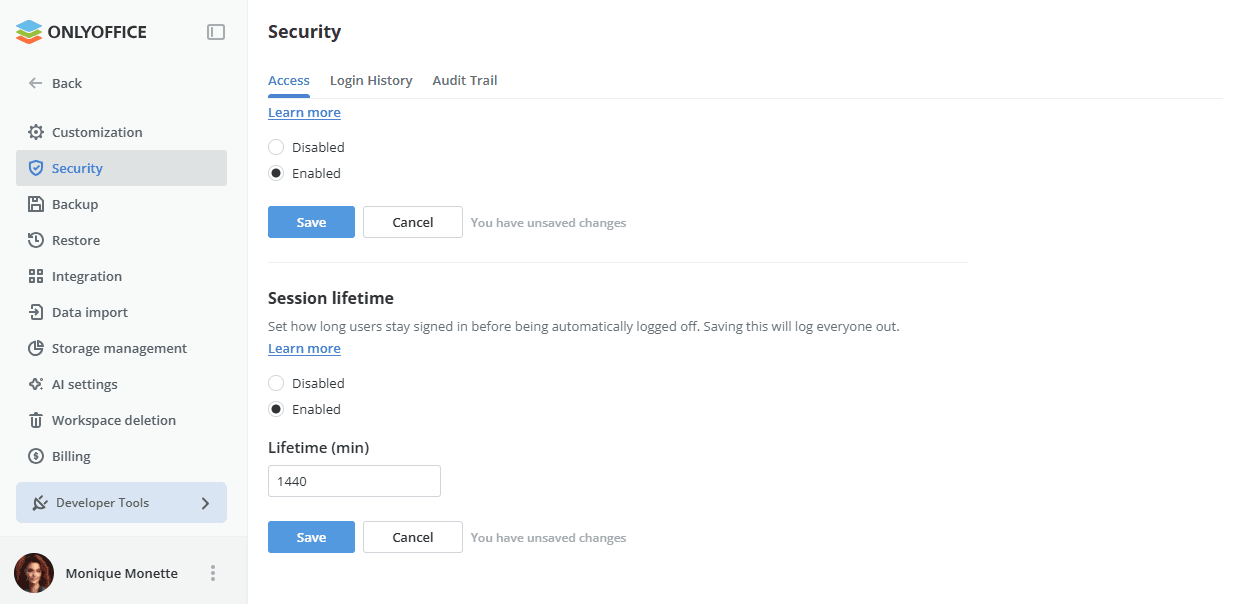
To set a session lifetime, check the Enabled radio button, enter the necessary time value measured in minutes in the Lifetime field that appears and click the Save button at the bottom of the section to apply the changes you made. Saving this will log everyone out.
When this setting is enabled, the Remember me checkbox will be hidden on the login page.
Invitations
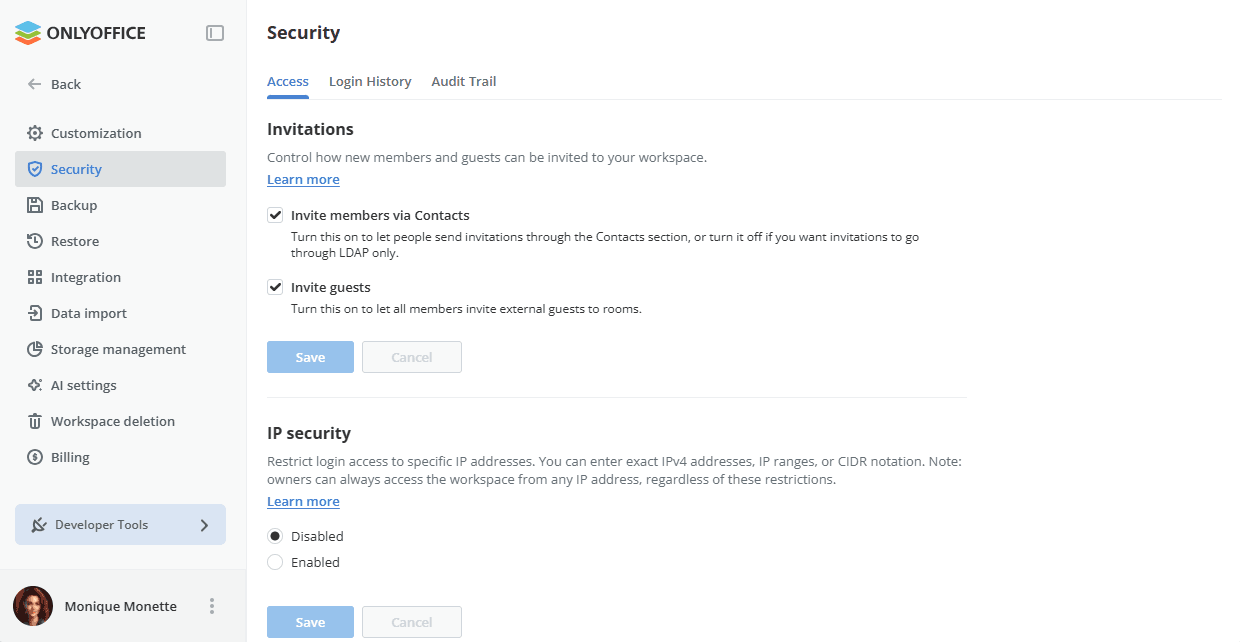
This section allows you to control how new members and guests can be invited to your workspace. These settings can help you comply with your company's security guidelines, for example, if you use LDAP or other user management systems. By default, all the invitation settings are enabled. Uncheck the options you want to disable:
-
Invite members via Contacts - turn this on to let people send invitations through the Contacts section, or turn it off if you want invitations to go through LDAP only.
When this option is disabled, the Invite option will be hidden in the Contacts section.
-
Invite guests - turn this on to let all members invite external guests to rooms.
When this option is disabled, it's not possible to add a new user with a non-existent email in the invitation panel within a room. In this case, only existing workspace users can be invited to a room.
Click the Save button at the bottom of the section to apply the changes you made.
IP security
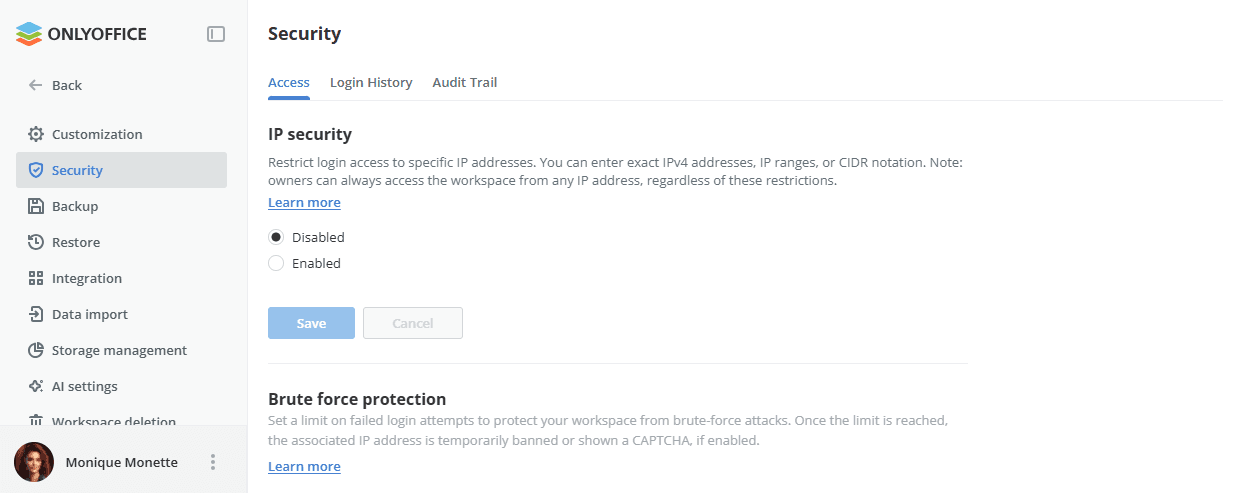
This section allows you to restrict login access to specific IP addresses. If a user attempts to log in to your workspace from any IP address except those you specify, this login attempt will be blocked. To restrict access based on the IP addresses,
-
check the Enabled radio button;
-
click the Add allowed IP address link;
-
in the entry field that appears, specify an exact IPv4 address (#.#.#.#, where # is a numeric value from 0 to 255), an IP addresses range by entering the starting and ending IP addresses of the range in the #.#.#.#-#.#.#.# format, or a subnet in the CIDR notation;
noteYou can find the information on your workspace visitors IP addresses in the Login History subsection of the Security settings by clicking the Download report button.
-
in the same way, add as many trusted IP addresses as you need;
-
click the Save button at the bottom of the section.
Owners can always access the workspace from any IP address, regardless of these restrictions.
If necessary, you can delete the added IP addresses by clicking the corresponding icon to the right of the IP address. To disable this option again, just check the Disabled radio button and click the Save button.
Tracking login history
The Login History subsection of the Security settings is used to monitor recent login activity, including successful logins and failed attempts, along with the reasons for each failure. In the SaaS version, this is a Paid feature (available for the paid Business plan only).
This page displays only the last 20 records. Each record shows the User who performed the action, the Date when the event occurred, and the Action that took place.
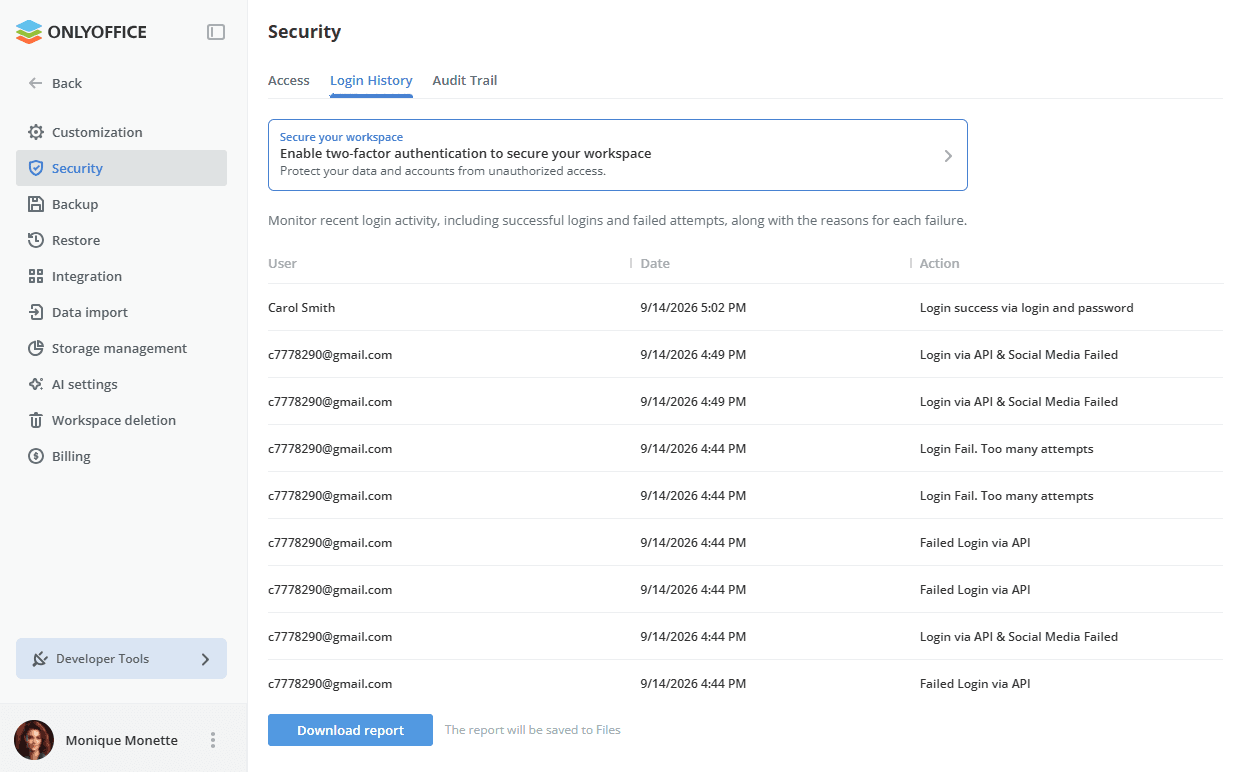
To view the detailed statistics for the latest half year, click the Download report button. The report will open in a .csv file (LoginHistory_ReportStartDate-EndDate.csv).
The report will also be saved to the Files app.
The login history report includes the following details: user IP address, Browser and Platform which were used when the registered event occurred, Date and time of the event, name of the User who made an attempt to log in/log out, Page where the action has been performed, specific Action (for example, Login Fail. Associated Social Account Not Found).
The records are sorted chronologically in descending order, but you can easily sort and filter the data by any parameter or use the search tool to quickly find a specific record.
Receiving audit trail data
The Audit Trail subsection of the Security settings allows you to browse a list of recent changes users have made across your workspace, like creating, editing, or deleting rooms, files, and other items. In the SaaS version, this is a Paid feature (available for the paid Business plan only).
This page displays only the last 20 records. Each record shows the User who performed the action, the Date when the event occurred, the Location where it took place, and the Action that was performed.
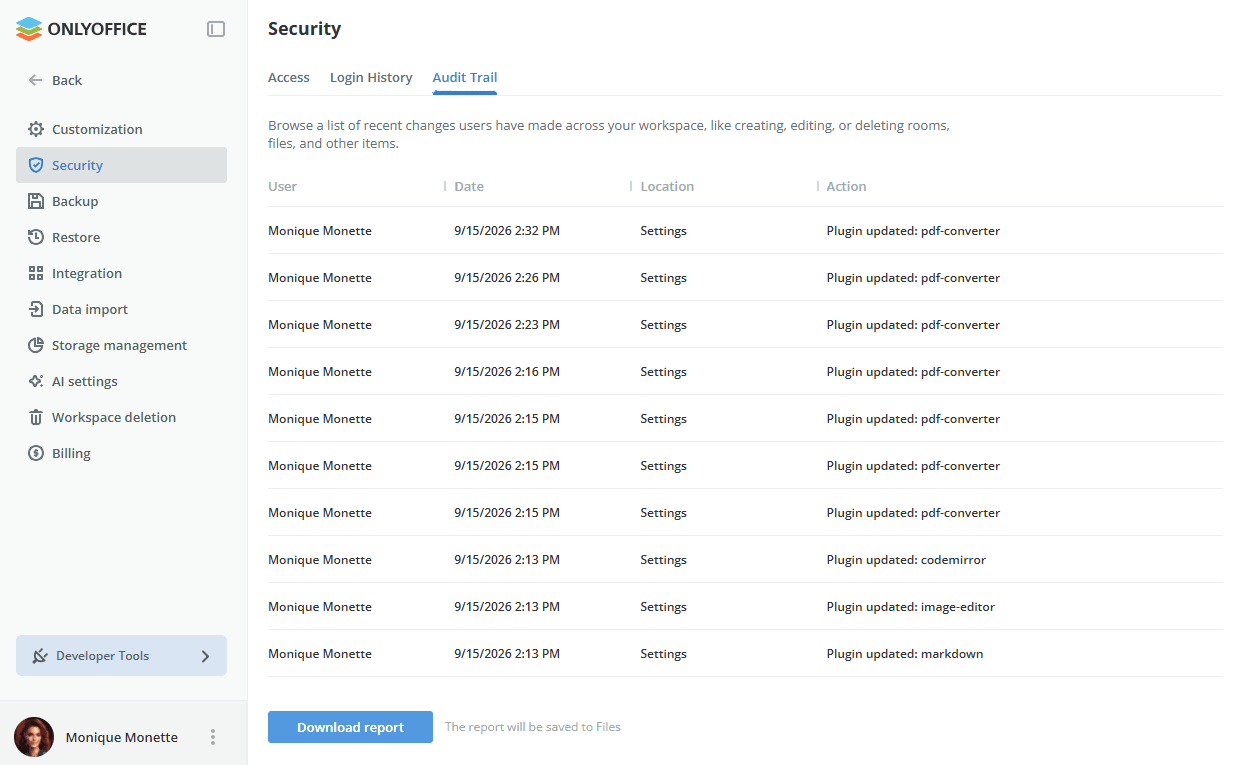
To view the detailed statistics for the latest half year, click the Download report button. The report will open in a .csv file (AuditTrail_ReportStartDate-EndDate.csv).
The report will also be saved to the Files app.
The audit trail report includes the following details: user IP address, Browser and Platform which were used when the registered event occurred, Date and time of the event, name of the User who performed the operation, Page where the action has been performed, generic Action Type (for example, download, updated access), specific Action (for example, File Uploaded: Timetable.ods), Product and Module that the changed entity is referred to.
The records are sorted chronologically in descending order, but you can easily sort and filter the data by any parameter or use the search tool to quickly find a specific record.